Australia’s Cybersecurity Website Hit by Critical Software Vulnerability
By Chloe · Published 22 Oct 2026 · Updated 22 Oct 2026
Canberra, ACT · ACT News
Safety note: Admin approval is an initial review, not a guarantee that every detail is correct. Check important or urgent claims with official sources and report anything inaccurate or unsafe.
Source and credit: Contributor's own report
Australia’s Cybersecurity Website Hit by Critical Software Vulnerability - Canberra, ACT
Smart summary
Australia’s cyber.gov.au website is among the government services affected by two critical vulnerabilities in PHP, a programming language used by millions of websites worldwide. Security agencies are urging organisati...
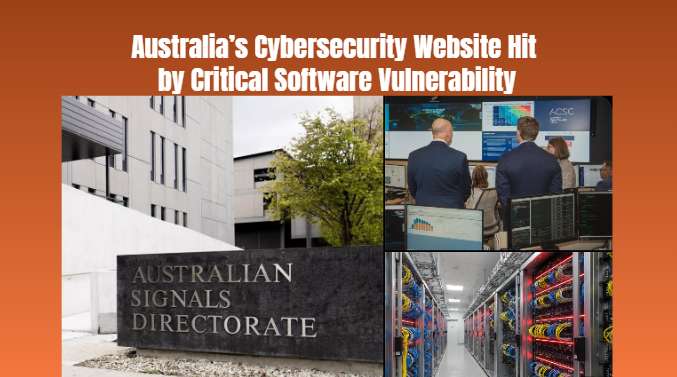
Australian cybersecurity authorities are responding to a serious software security issue that could put websites and internet-connected systems at risk. The Australian Signals Directorate (ASD), which oversees the Australian Cyber Security Centre (ACSC), confirmed that the national cybersecurity website, cyber.gov.au, was among the Australian government services affected by the reported PHP vulnerabilities.
The issue was reported by ABC News on Thursday, 22 October 2026. PHP is a widely used programming language that helps websites process information, display pages and run applications. It supports major content-management platforms and online services, meaning vulnerabilities in the software can potentially affect a large number of websites.
What is the software flaw? Developers have identified two critical vulnerabilities in PHP. Security researchers and technology companies have warned that attackers may be able to exploit vulnerable systems, potentially allowing unauthorised activity on affected servers.
PHP is used by platforms such as Word Press, Drupal, Joomla and Magento. Many organisations rely on these technologies for publishing news, managing customer information, operating online stores and delivering public services.
Because the software is so widely deployed, a serious vulnerability can create a significant challenge for security teams. Organisations need to identify which systems use affected PHP versions, assess their exposure and apply the relevant security updates as soon as they become available.
The vulnerabilities have been associated in media reporting with the identifiers CVE-2026-109618 and CVE-2026-109619. However, the ACSC's initial alert said full technical details were scheduled for release on 22 October and warned that versions from PHP 5 onwards might be affected.
Government and international response The warning extends beyond Australia. ABC News, citing international reporting, said government departments and major online services overseas were also affected. Some organisations temporarily took websites offline as a precaution while preparing to install fixes.
The incident demonstrates how a vulnerability in widely shared software can affect organisations in multiple countries simultaneously. Even services that operate independently may rely on the same underlying programming language or software components.
The Australian Signals Directorate has urged organisations and individuals running PHP applications to monitor official guidance and apply security patches when released.
Importantly, the ACSC's initial advisory said it was not then aware of active exploitation related to the vulnerabilities. Media reports have separately described concerns about potential exploitation, so the precise extent of confirmed attacks should not be overstated.
What should website owners do? Security specialists recommend that organisations: - Identify servers, websites and applications running PHP. - Monitor official PHP security announcements for updates. - Apply the relevant patches promptly once available. - Review server logs and monitor for suspicious activity. - Consider additional protective measures if systems cannot be updated immediately. Website owners should obtain updates from official PHP sources or their hosting providers rather than downloading unfamiliar patches from third-party websites. Why this matters The vulnerability highlights the importance of maintaining software, even when it operates behind the scenes. A website can have strong passwords and other security controls but still be exposed if the software powering it contains a critical flaw.
For Australian businesses, government departments and website operators, identifying affected systems and responding quickly will be essential to reducing the risk of disruption or unauthorised access.
SecuritySoftwareAffectedOrganisationsWebsite
Australian cybersecurity authorities are responding to a serious software security issue that could put websites and internet-connected systems at risk. The Australian Signals Directorate (ASD), which oversees the Australian Cyber Security Centre (ACSC), confirmed that the national cybersecurity website, cyber.gov.au, was among the Australian government services affected by the reported PHP vulnerabilities.
The issue was reported by ABC News on Thursday, 22 October 2026. PHP is a widely used programming language that helps websites process information, display pages and run applications. It supports major content-management platforms and online services, meaning vulnerabilities in the software can potentially affect a large number of websites.
What is the software flaw? Developers have identified two critical vulnerabilities in PHP. Security researchers and technology companies have warned that attackers may be able to exploit vulnerable systems, potentially allowing unauthorised activity on affected servers.
PHP is used by platforms such as Word Press, Drupal, Joomla and Magento. Many organisations rely on these technologies for publishing news, managing customer information, operating online stores and delivering public services.
Because the software is so widely deployed, a serious vulnerability can create a significant challenge for security teams. Organisations need to identify which systems use affected PHP versions, assess their exposure and apply the relevant security updates as soon as they become available.
The vulnerabilities have been associated in media reporting with the identifiers CVE-2026-109618 and CVE-2026-109619. However, the ACSC's initial alert said full technical details were scheduled for release on 22 October and warned that versions from PHP 5 onwards might be affected.
Government and international response The warning extends beyond Australia. ABC News, citing international reporting, said government departments and major online services overseas were also affected. Some organisations temporarily took websites offline as a precaution while preparing to install fixes.
The incident demonstrates how a vulnerability in widely shared software can affect organisations in multiple countries simultaneously. Even services that operate independently may rely on the same underlying programming language or software components.
The Australian Signals Directorate has urged organisations and individuals running PHP applications to monitor official guidance and apply security patches when released.
Importantly, the ACSC's initial advisory said it was not then aware of active exploitation related to the vulnerabilities. Media reports have separately described concerns about potential exploitation, so the precise extent of confirmed attacks should not be overstated.
What should website owners do? Security specialists recommend that organisations: - Identify servers, websites and applications running PHP. - Monitor official PHP security announcements for updates. - Apply the relevant patches promptly once available. - Review server logs and monitor for suspicious activity. - Consider additional protective measures if systems cannot be updated immediately. Website owners should obtain updates from official PHP sources or their hosting providers rather than downloading unfamiliar patches from third-party websites. Why this matters The vulnerability highlights the importance of maintaining software, even when it operates behind the scenes. A website can have strong passwords and other security controls but still be exposed if the software powering it contains a critical flaw.
For Australian businesses, government departments and website operators, identifying affected systems and responding quickly will be essential to reducing the risk of disruption or unauthorised access.
George Town, Tasmania · Technology News · 10 Oct 2026
Tasmania’s environmental regulator is seeking to participate in a tribunal appeal after concerns that a proposed AI data centre could use hundreds of di...
The federal government says artificial intelligence companies could be required to prove that their AI systems are properly tested and capable of preven...
A Queensland government department has lost approximately $800,000 in a cyberattack, prompting a review that found no government data or sensitive infor...
New evidence indicates autonomous Open AI agents attempted to access information from several Australian government and public-sector websites, expanding...
The Australian Federal Police says threats and harassment targeting federal politicians and senior public officials have increased sharply, raising fres...
One Nation leader Pauline Hanson has apologised after a controversial political cartoon mocked independent senator Jacqui Lambie’s medical condition, sa...
Australian biofuel producers are urging the federal government to require fuel companies to purchase more locally produced ethanol and biodiesel, after...
A new Australian Human Rights Commission report calls for stronger workplace protections after workers reported losing jobs, shifts and promotion opport...
Australian workers and industry representatives are calling for stronger action by the Australian Taxation Office after new reporting highlighted that a...
A new report from the Australian Institute of Health and Welfare reveals a sharp rise in hospital admissions involving electric scooters and other power...
A 29-year-old man was arrested after allegedly attempting to steal a vehicle while carrying an axe following a multi-vehicle collision in Melbourne’s no...
A court has heard evidence from a friend of former police officer Beau Lamarre-Condon during his trial over the alleged murders of Jesse Baird and Luke...